N-able Releases Second N-Central Hotfix as Attacks Escalate
N-able issued a mandatory second hotfix for CVE-2026-18577 after threat actors evolved attack techniques to reach managed endpoints via Cloudflare Tunnels.
N-able issued a mandatory second hotfix for CVE-2026-18577 after threat actors evolved attack techniques to reach managed endpoints via Cloudflare Tunnels.
A multi-wave campaign uses fake Adobe and Zoom update lures to deploy ConnectWise ScreenConnect. A separate campaign distributes the Powercat Java stealer via f
A critical flaw in Rails' Active Storage framework allows unauthenticated file reads and potential RCE. Patch immediately and rotate all secrets.
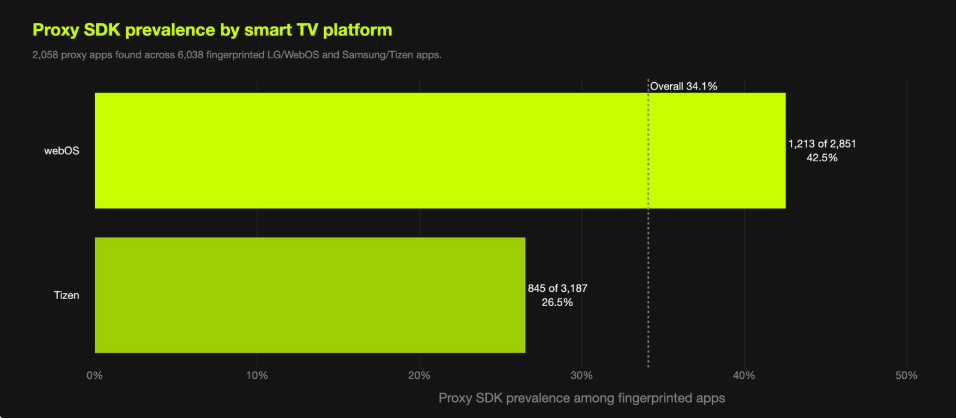
LG Electronics will suspend smart TV apps that turn televisions into residential proxy nodes, following research showing over 42% of webOS apps contained proxy
Microsoft fixed 570 vulnerabilities in July's Patch Tuesday, nearly triple last month's record. AI-assisted discovery is driving the surge in patch volume.
OpenAI is temporarily lifting GPT-5.6 Sol's five-hour usage cap for Plus, Pro, and Business plans and issuing a one-time usage reset.
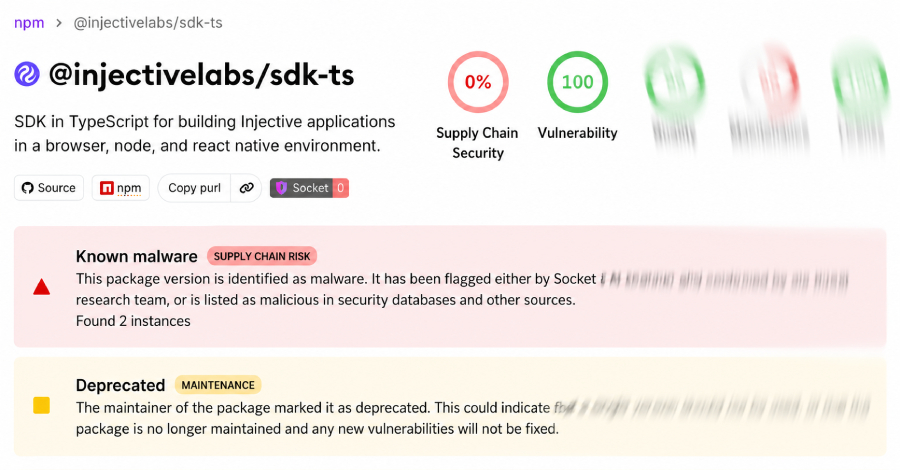
Attackers compromised the Injective Labs GitHub repository to publish a malicious npm package that exfiltrates private keys and mnemonic phrases.
AI is rapidly widening the gap between skill and ability in cyberattacks. The same tools that strengthen defense also enable harm.
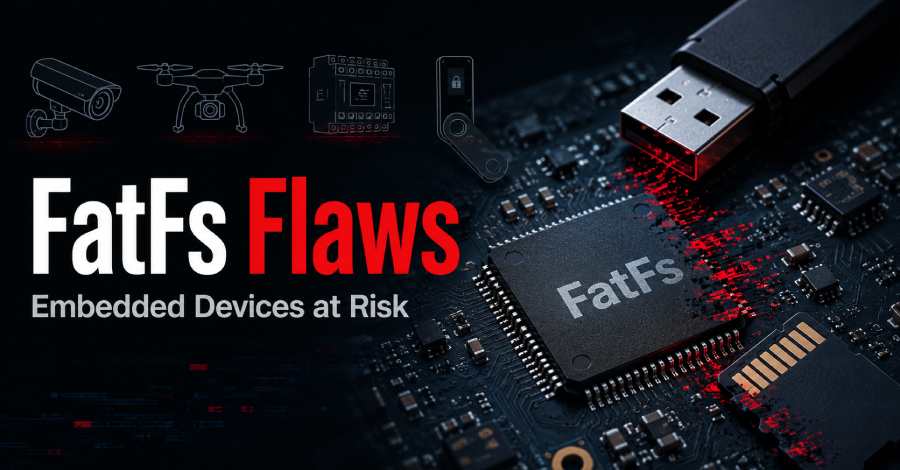
Security firm runZero disclosed seven vulnerabilities in FatFs, a filesystem library embedded in cameras, drones, and industrial controllers. No upstream fix ex
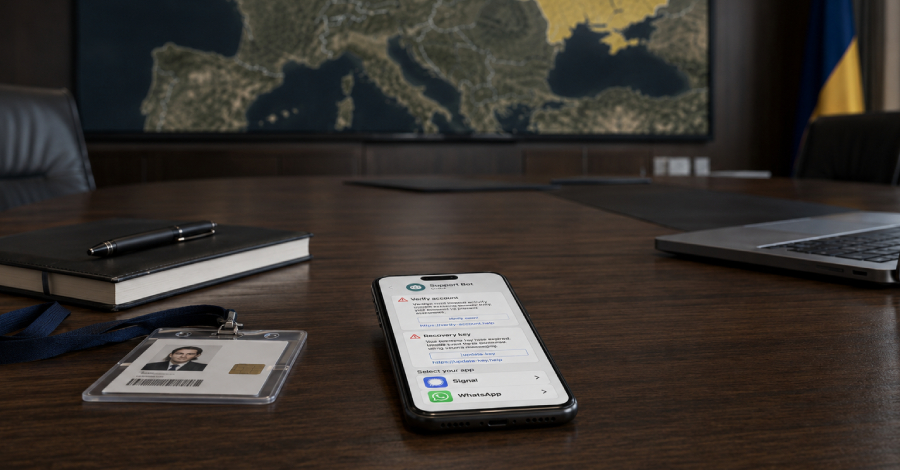
Russia targeted Signal and WhatsApp accounts of officials and activists across Ukraine, Europe, and the U.S. via SMS phishing posing as platform support bots.
45% of SMBs suffered a cyber incident last year, yet confidence in resilience has surged. Here's where readiness stands and what comes next.
BleepingComputer hosts a July 8, 2026 webinar on account takeover threats and how behavioral AI can automate detection and response.