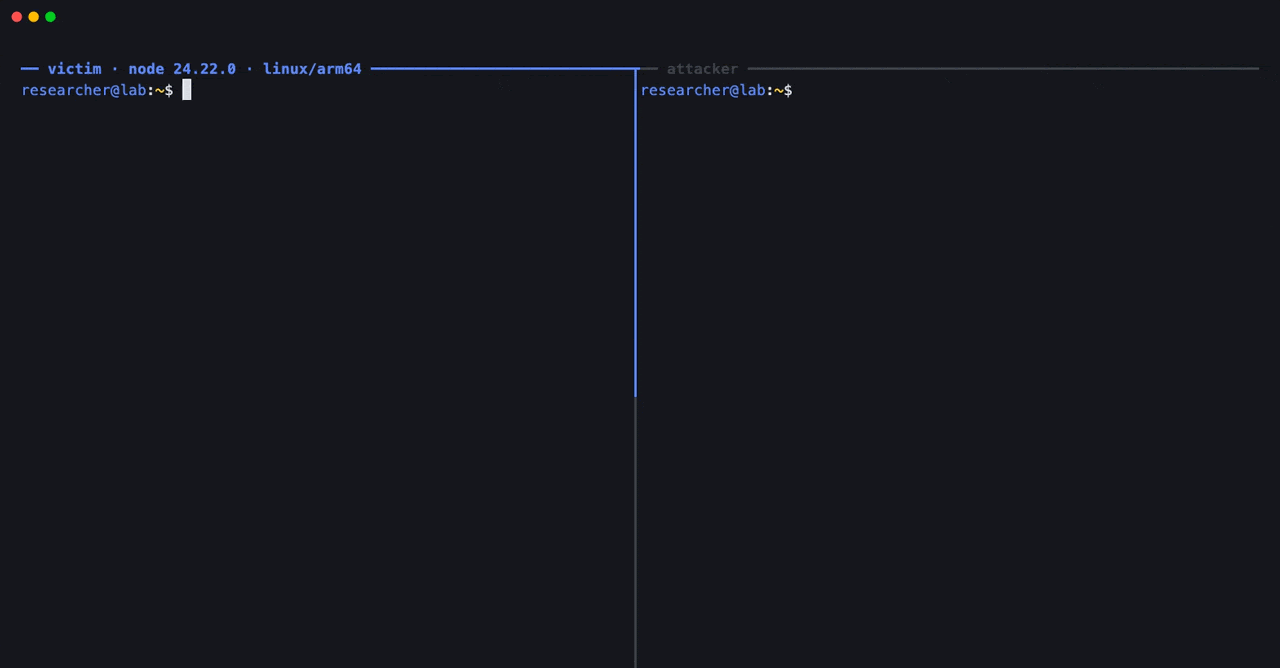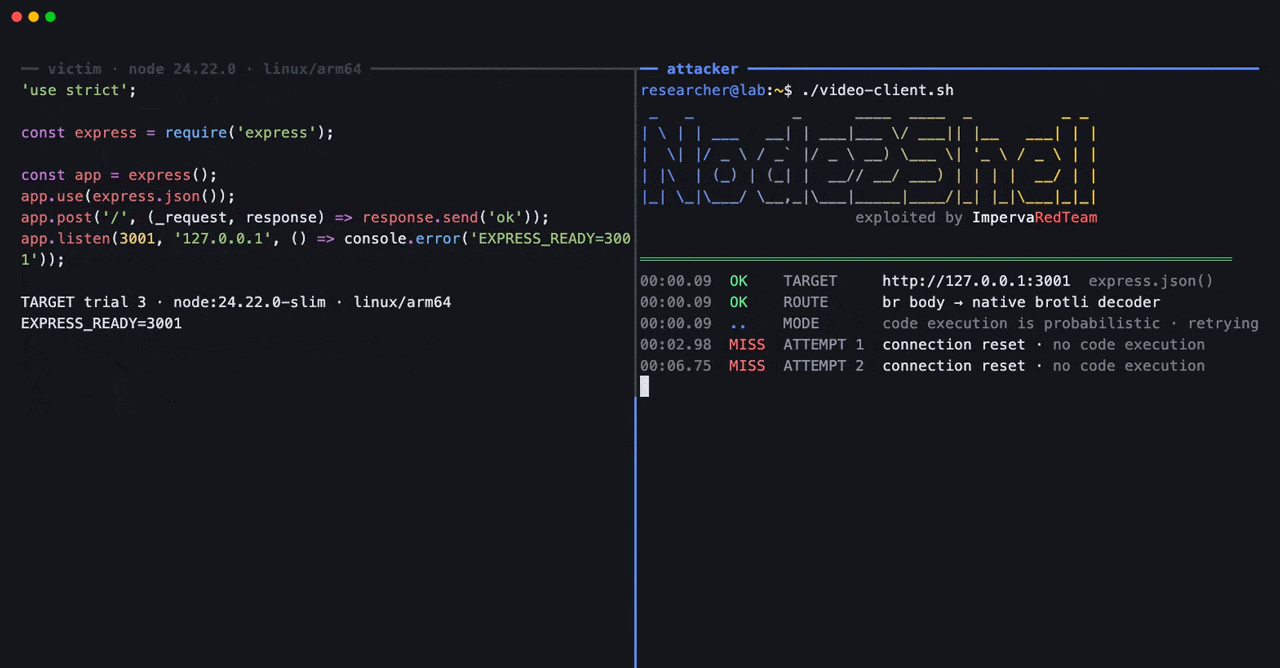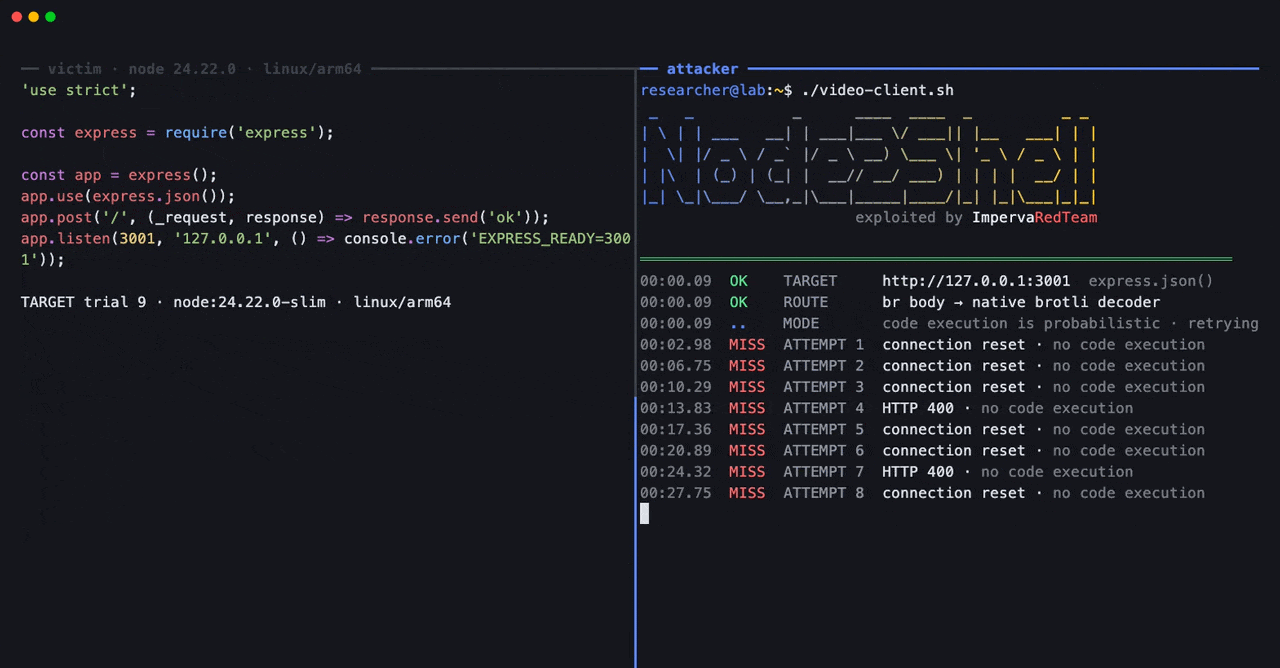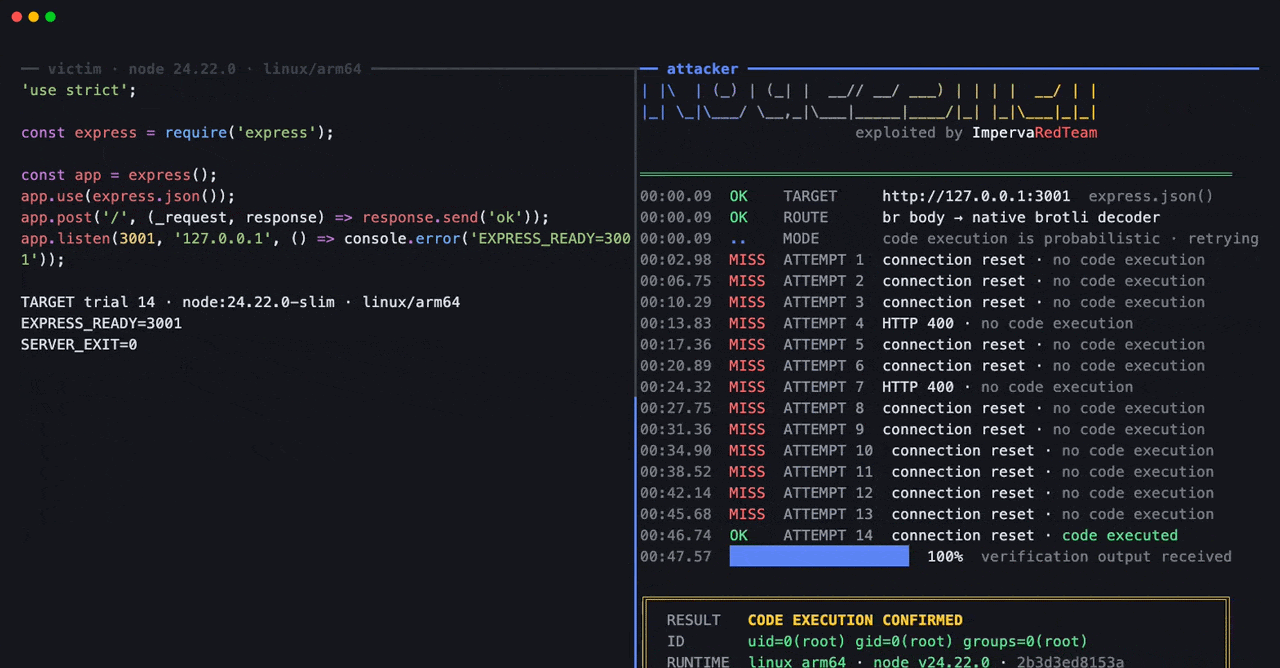
Node2Shell PoC Achieves RCE on Official Node.js via Brotli Bug
Imperva's Node2Shell proof of concept executes attacker code on an official Node.js 24 build via a Brotli decoder flaw. Patches were released October 21.
Imperva's Node2Shell proof of concept executes attacker code on an official Node.js 24 build via a Brotli decoder flaw. Patches were released October 21.
A compromised ConnectWise Cloud Backup credential has been used to gain unauthorized access to 173 partner and customer Microsoft 365 tenants.
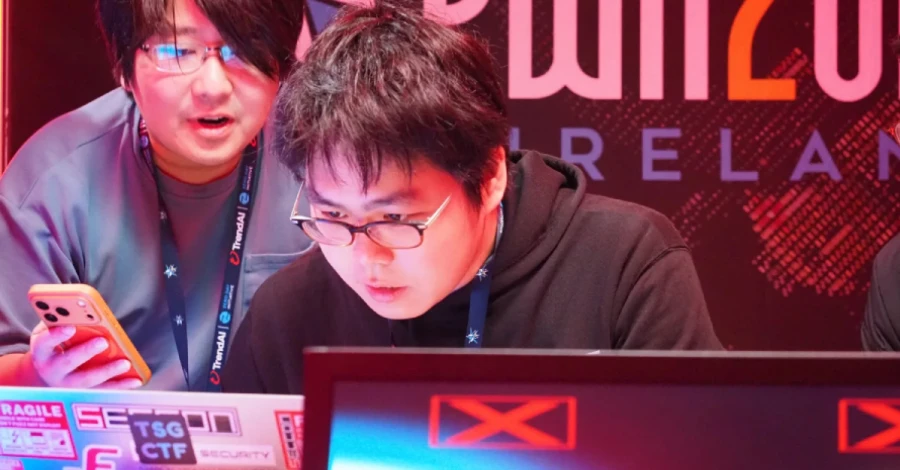
Three research teams successfully exploited a fully patched Google Pixel 10 at Pwn2Own Ireland, winning a combined $562,500 in prizes.
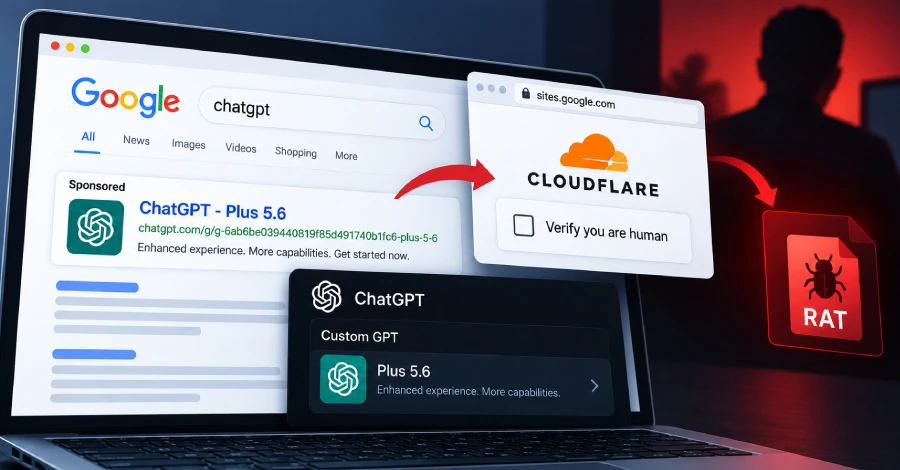
Threat actors are weaponizing ChatGPT Custom GPTs to redirect victims to ClickFix lures that deploy a full-featured remote access trojan via DLL sideloading.
Identity visibility is foundational to modern security. This guide covers core concepts, cloud challenges, and leading platform capabilities.
AI-powered nudify apps are a growing threat. Here's how to reduce your risk and respond if you or your child becomes a victim.
James Strahler II was sentenced to 15 years for cyberstalking, AI-generated sextortion, and child sexual abuse material. He is the first person convicted under
Microsoft is fixing a bug causing Teams and new Outlook to crash on ARM devices after August 2026 Patch Tuesday updates. A temporary workaround is available.
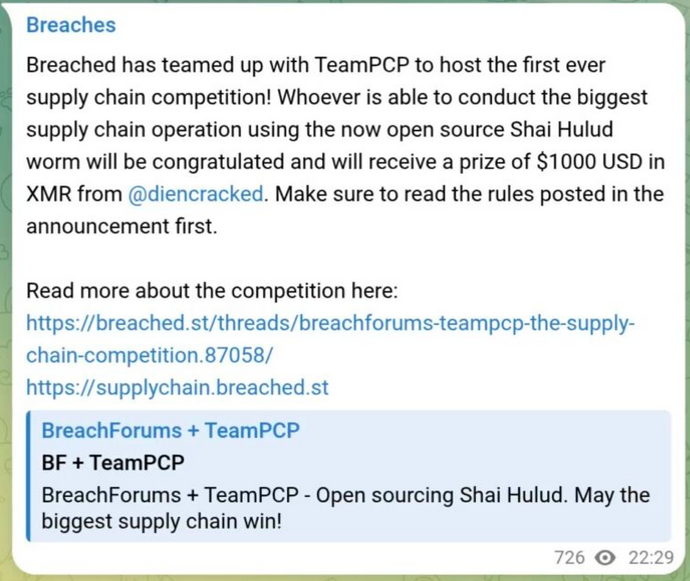
Australian Federal Police arrested two Western Australia men linked to TeamPCP, a cybercrime group behind a sweeping software supply chain attack campaign.
ToxicPanda 2.0 adds 167 remote commands and targets 349 financial institutions. GoldDigger expands to South Africa and the U.K. via fake airline and retail apps
A critical GitLab flaw rated CVSS 9.4 requires no authentication to exploit. Self-managed users should patch immediately or restrict GraphQL access.
Two new papers examine how LLMs fail to control sensitive information flow based on context, and how reasoning and reinforcement learning may help.