Node.js Patches 16 Flaws, Including HTTP/2 Crash and Memory Leaks
Node.js fixed 16 flaws, seven rated high, including HTTP/2 crash and memory leaks. Updating to 22.23.5, 24.22.3 or 26.13.1 is the only fix.
Node.js fixed 16 flaws, seven rated high, including HTTP/2 crash and memory leaks. Updating to 22.23.5, 24.22.3 or 26.13.1 is the only fix.
ESET details Gorbag, a Russia-aligned actor hitting Ukrainian justice, local and defense targets. It favors one-pass data theft over long-term access.
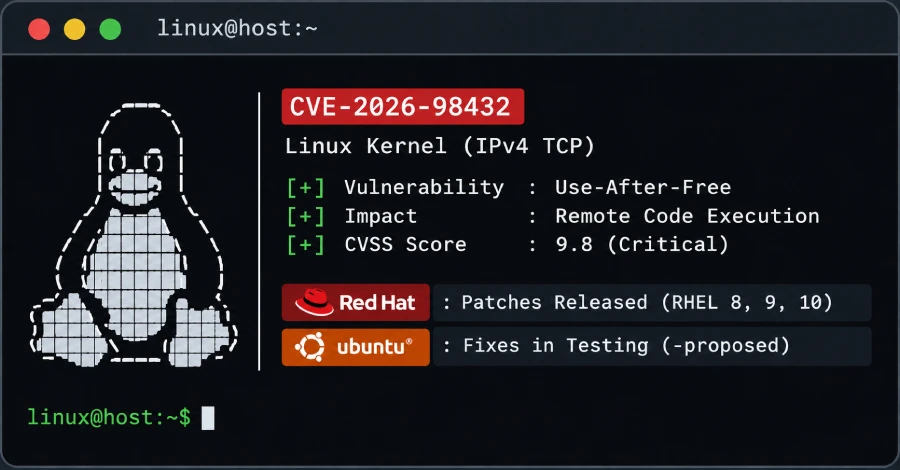
CVE-2026-98432, a remotely exploitable use-after-free in Linux's IPv4 TCP code, has been patched in RHEL 8, 9, and 10. Ubuntu fixes remain in testing.
Trump was briefed on a Chinese intelligence operation targeting Nvidia's CEO but took no action. Federal data security lapses compound the risk.
Google's Registered App Stores program lets approved third-party stores install and update Android apps with one tap, launching December 1 outside the US.
Agentic pentesting is the sharpest edge of offensive security today, but it leaves critical gaps. Here's where those blind spots are and how to address them.
Breach notices are revealing less than ever. Here's how to interpret vague notifications and take meaningful action to protect yourself.
The Wazza phishkit targets banking, manufacturing, and government sectors across the US, Europe, and Australia using a multi-stage routing chain to evade detect
A teenager suspected of leading ShinyHunters was detained in Jordan while extorting a former Boeing subsidiary, and is now cooperating with the FBI.
A phishing platform impersonates AI chatbot ad products to steal credentials and MFA codes via browser-in-the-browser attacks targeting agency ad accounts.
UNC6240 is mass-exploiting CVE-2026-35273 in Oracle PeopleSoft by URL-encoding requests to bypass WAF rules, deploying web shells and backdoors across multiple
Vectra AI announced Ascent, a global partner program built to help customers address AI-driven security threats through expertise, services, and joint capabilit