The Browser Is Now Where Breaches Begin and Go Undetected
The 2026 Verizon DBIR confirms what browser telemetry has shown for months: the browser is the primary attack surface most enterprises aren't watching.
The 2026 Verizon DBIR confirms what browser telemetry has shown for months: the browser is the primary attack surface most enterprises aren't watching.
BTMOB is an Android RAT evolved from SpySolr, sold as a MaaS kit with phishing tools and full device takeover capabilities targeting users across Latin America.
CVE-2026-3300 in Everest Forms Pro lets unauthenticated attackers run arbitrary PHP and create rogue admin accounts.
A dark web tutorial by "Hercules" breaks vulnerability exploitation into steps any beginner can follow - and it's spreading fast.
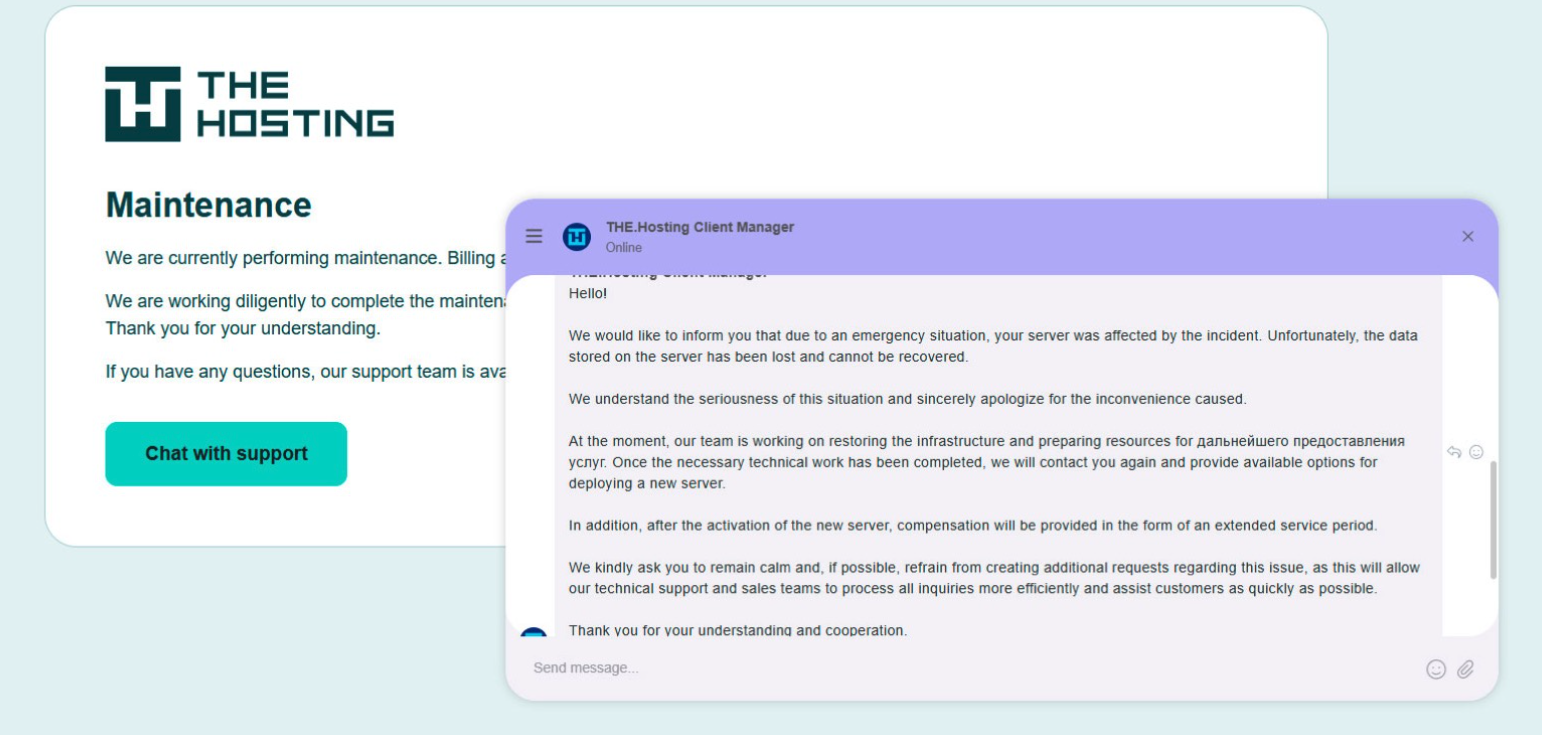
Dutch authorities arrested two hosting company co-owners and seized 800 servers tied to Russian cyberattacks and disinformation operations inside the EU.
A new skimming campaign routes stolen payment data through api.stripe.com, bypassing CSP filters by abusing trusted infrastructure.
A flaw in Claude Code's GitHub Action let any attacker with a bot account hijack public repos and steal write credentials via prompt injection.
DentaQuest's breach exposed 2.6 million accounts including health IDs and insurance data after ShinyHunters published 234 GB when negotiations collapsed.
A high-severity zero-day in Cisco Catalyst SD-WAN Manager lets low-privilege attackers escalate to root. No patch is available yet.
Fake FIFA domains, banking trojans in streaming apps, and a single Chinese-speaking operation running 300 cloned login pages - all live before June 11.
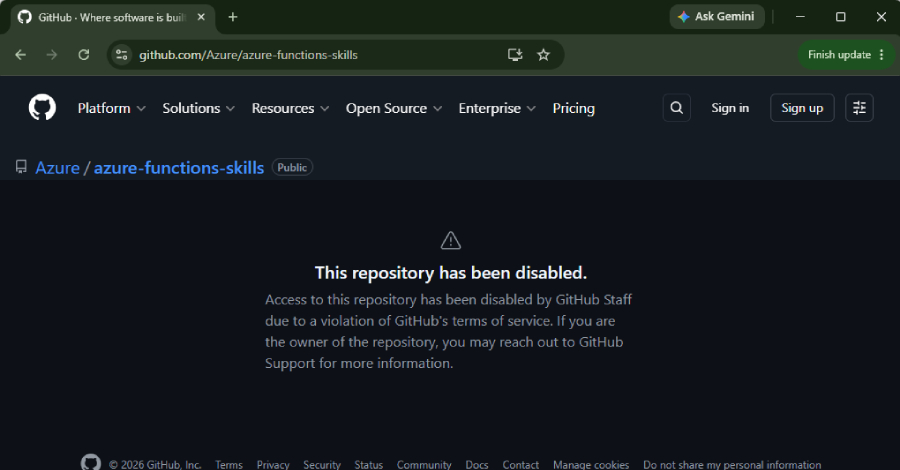
A self-replicating worm has compromised 73 Microsoft GitHub repositories across Azure, MicrosoftDocs, and related orgs, disabling developer access.
A Rust-based infostealer called IronWorm compromised 36 npm packages, targeting AWS, OpenAI, and SSH credentials via a stealthy supply-chain attack.