AI Agents Can Find Exploits From Rumors Alone
AI agents can locate vulnerabilities with only a vague description of a bug. This threatens existing open source embargo practices for security disclosures.
AI agents can locate vulnerabilities with only a vague description of a bug. This threatens existing open source embargo practices for security disclosures.
ESET researchers discovered a technique that uses a decoy comment to trigger LLM safety guardrails and halt AI-assisted malware analysis before it reaches malic
Threat actors call employees on personal devices, steal Microsoft credentials, then use the Graph API to quietly exfiltrate corporate data at scale.
Microsoft's September Patch Tuesday fixes 974 vulnerabilities—its largest ever. Two actively exploited zero-days and 113 critical flaws are included.
A breach at Trezor's shipping provider ShipMonk has grown to affect 81,000 customers after the provider failed to delete data as contractually required.
A dark web service called Nexus is selling scans of 153 million North American drivers licenses. Evidence points to a breach at Louisiana-based identity verific
A price-manipulation attack on Tectonic drained $74 million in borrowed assets. Cronos halted and restored the blockchain to a pre-exploit state.
AI tools let cybercriminals profile victims faster and cheaper than ever. Here's what the threat looks like and what you can still control.
A ransomware affiliate called Ransom Busters is charging victims $20,000–$60,000 to delete their stolen data, while posing as a helpful third party.
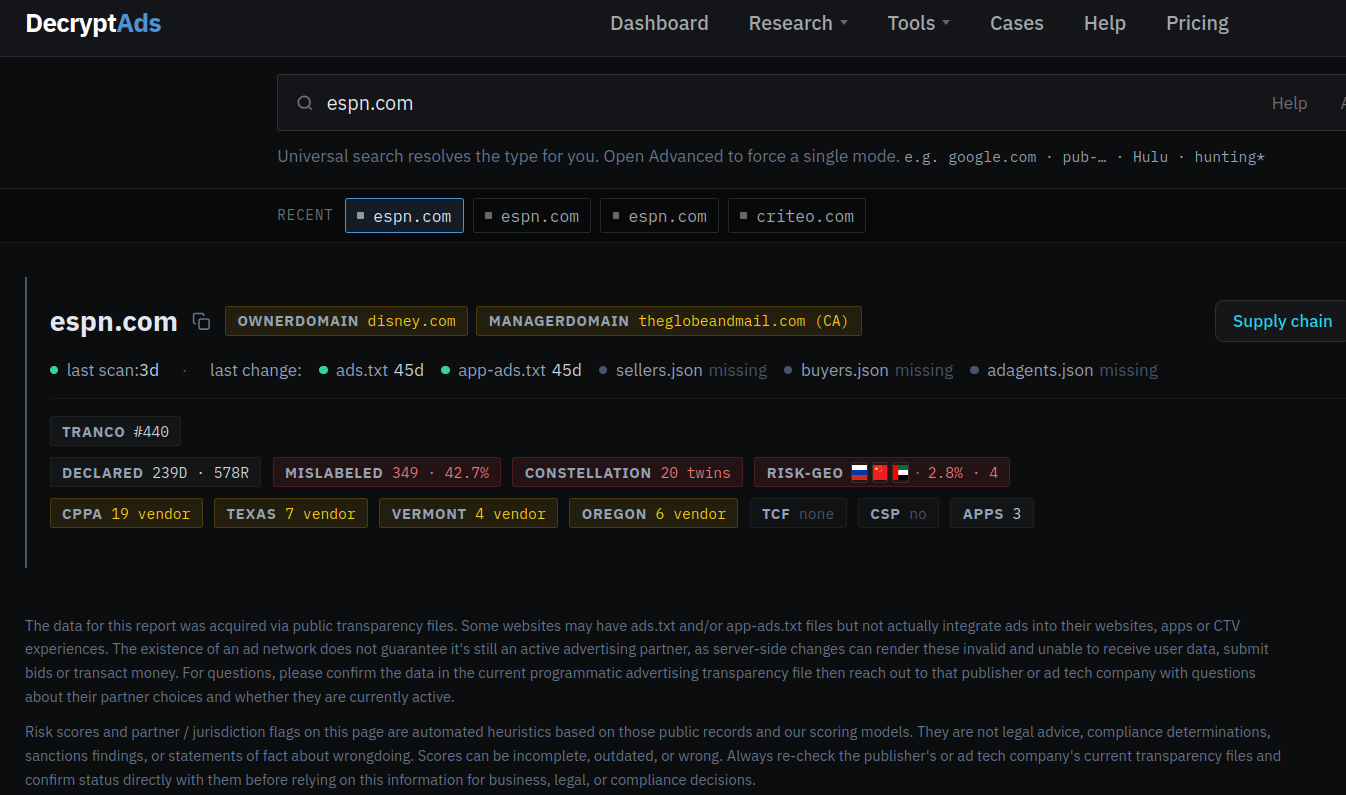
A free service called DecryptAds scrapes public adtech files to show which companies track users across websites and apps, flagging high-risk ad partners.
Laundry Bear is exploiting a zero-day XSS flaw in Exchange OWA to deploy the OWAReaper backdoor, enabling persistent mailbox access that survives credential res
Check Point has patched three vulnerabilities, including a critical actively exploited authentication bypass in SmartConsole. CISA has added the flaw to its KEV