Cybersecurity has never been easy. Threats evolve at breakneck speed. Corporate attack surfaces continue to expand with each new digital investment. Regulatory requirements add extra pressure on stretched teams. And behind it all, the unpredictability of human nature means there is no such thing as 100% security. But the market for security solutions doesn’t make things any easier for SMBs.
Smaller organizations usually have fewer resources and less expertise to throw at the problem than their larger counterparts. But they absolutely understand the need for advanced protection. It’s just that they also want it to feel simple, guided and manageable. Solutions and services that foreground such an approach are in short supply. But they do exist.
SMBs Understand the Importance of Cybersecurity
“Good enough” security is simply not good enough at a time of persistent geopolitical uncertainty and rapid technological change. ESET data reveals that three-quarters (75%) of SMBs are concerned about global conflicts and cyber warfare. And nearly half have experienced at least one cyber incident in the past year.
Whether it’s Iran-nexus threat actors targeting British power and US water plants, or, as shown by recent ESET research, Russia-aligned hackers hitting Polish energy facilities, state-backed attacks are more frequent and more ambitious than they’ve ever been. SMBs are very much in the crosshairs, as providers of critical infrastructure themselves or suppliers to firms operating in critical infrastructure.
But that’s only half the picture. Financially motivated groups continue to pose an outsized threat, usually via ransomware or data theft extortion. Often they operate with impunity from hostile states, where they elude the reach of Western law enforcement agencies. There’s growing evidence to suggest they even collaborate with government hackers on some campaigns.
Yet the identity of the adversary is arguably less important than the tactics they’re using to target global SMBs. AI is empowering threat actors everywhere to upskill and scale attacks more cost effectively than before. They’re moving through the attack chain at speed, from reconnaissance to exfiltration, collapsing the vulnerability exploitation window, and building highly convincing personalized phishing messages.
A new wave of autonomous agent-powered attacks will come next. We know what they’re capable of, because they’ve already broken free of vendor testing environments to socially engineer victims, create fake personas, exploit weak passwords, and deploy malicious code. If rogue agents can do this, then deliberately manipulated agentic AI can too.
AI is also the target. As SMBs embrace coding agents, chatbots and AI-assisted workflows, these tools are creating a new attack surface. Do you know what you’re running in your organization? Can you be sure it’s not being manipulated by malicious third parties? And are your users following policy when they interact with the technology? A third (32%) of North American and even more (42%) European organizations admit to having no rules in place to restrict the use of AI applications outside approved processes or platforms.
Overwhelmed and Overpriced
Against this backdrop, it’s perhaps not surprising that ESET finds that 58% of SMBs believe they are more vulnerable to cyber attacks than larger enterprises. It’s not just that they’re facing an unprecedented threat landscape. The pressure is operational as well as technical.
SMBs often struggle to make sense of a market crammed with industry jargon, competing marketing claims, and point solutions which address only narrow problems. They buy more technology, but the outcomes don’t improve.
The average company might use scores of siloed security tools, all pushing out alerts and impressive-looking dashboards. That does nothing but create more operational overhead, alert fatigue, and training gaps. Without the time, skills and confidence to manage all that technology, SMBs can quickly become overwhelmed. Real threats slip through the net while teams waste valuable time chasing false positives. Critical security updates are left undeployed while teams patch non-essential systems. Important tools are misconfigured.
Reducing the Burden
Smaller organizations want better protection, not another security puzzle to solve. They need tools and services they understand; that are simple to operate and deliver plain-language guidance and explanations on how they work and what they’re doing under the covers. They want 24/7/365 monitoring to ensure that any threat at any time can be caught and contained as soon as possible, reducing the impact on the organization. And they want expert help to understand what threats to prioritize when alerts are flying in and context is in short supply.
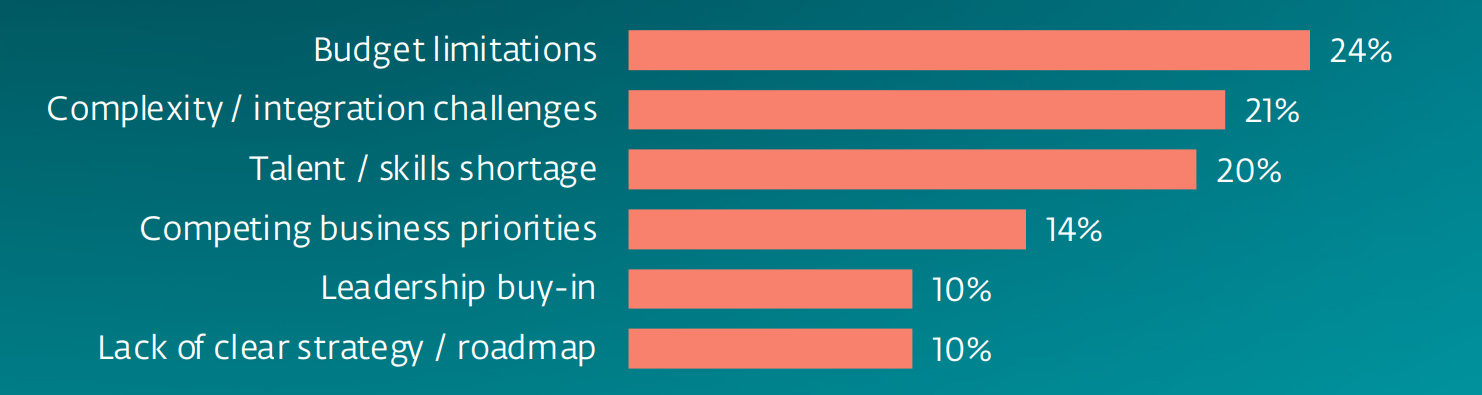 Barriers to better cybersecurity (source: ESET SMB Cyber Readiness Index 2026)
For many, this will mean outsourcing some parts of the security function to a trusted partner. They may not know the search term. But for many, the destination should be managed detection and response (MDR), which reduces the burden on in-house teams while ensuring no alert is missed. Yet historically, the SMB market has not necessarily been well served by MDR providers.
Smaller organizations may have felt locked out of a market that often charges a premium for their capabilities. After all, in-house 24/7 monitoring and threat hunting doesn’t come cheap, especially during a time of skills shortages.
Then there’s onboarding. Despite offering simplicity on the surface, many MDR offerings don’t work out like that in practice. They require integration with multiple systems and data sources, the granting of the correct permissions to outsourced SOC staff, the fine-tuning of detection rules, incident response planning, and many other complex, time-consuming tasks.
What most SMBs want is continuous monitoring, detection of suspicious activity, clear guidance on next steps, and experts on hand to help with containment and remediation as required. But in reality, it can be much more complicated.
For SMBs, this is about finding value for money: security that delivers the outcomes it promises. This matters more than ever at a time of continued business uncertainty, and the threat of cyber disruption which could have lasting consequences.
All organizations have to assume that they’ll be breached at some point in the future, no matter how effective their preventative controls. The key to avoiding potentially crippling financial and reputational damage is to contain and recover from any attack as quickly as possible. That means finding security that helps them make better decisions, not security that creates more work.
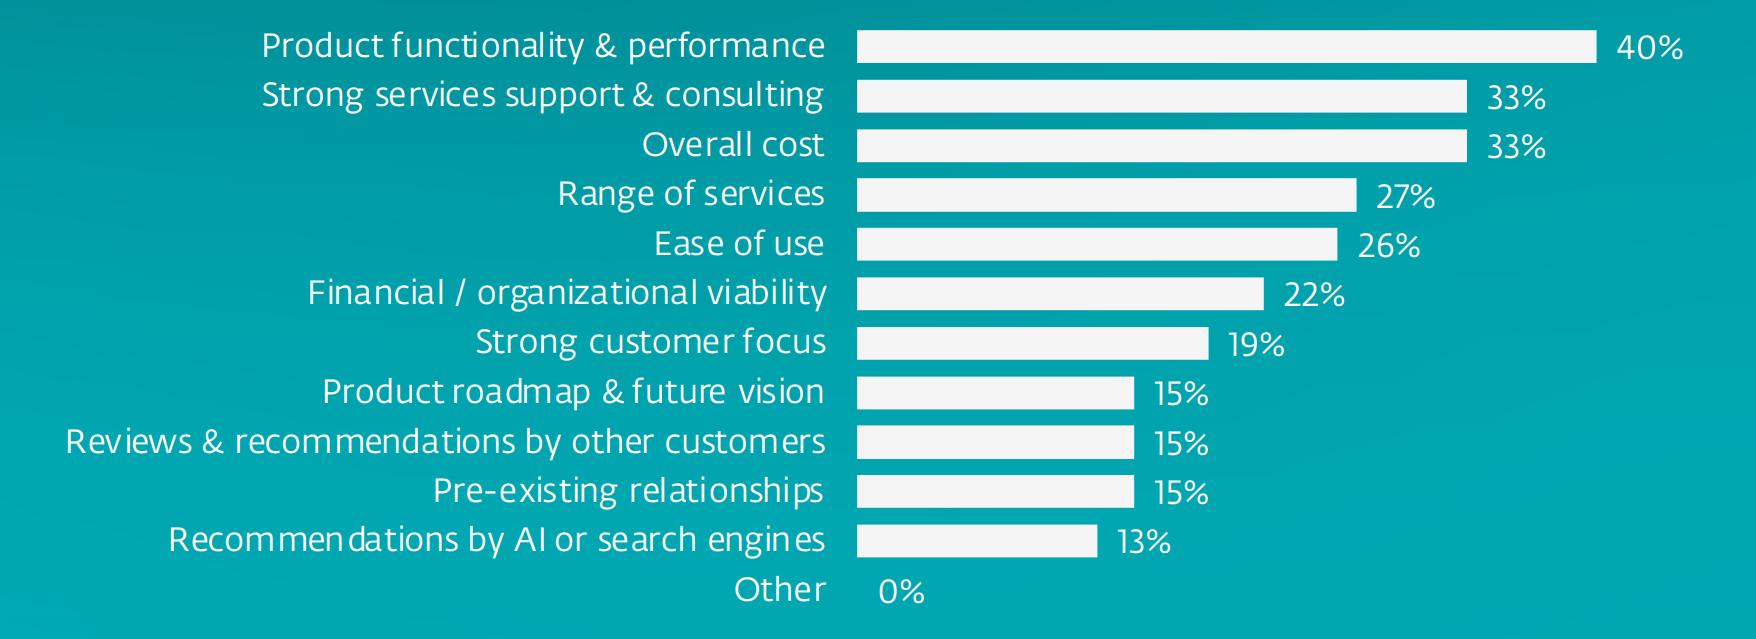 What matters when choosing a cybersecurity solution (source: ESET SMB Cyber Readiness Index 2026)
What SMBs Want
Against this backdrop, SMBs are looking for several complementary capabilities from their security partners. They want products and services that help to:
-
Lower the operational burden by absorbing the day-to-day work that in-house teams are struggling to get through. A provider might do this by automating routine processes such as remediation of common issues, by offering teams AI assistance to improve productivity, and by ensuring there’s always expert help for things like onboarding and intervening when AI and automation don’t deliver.
-
Detect and contain threats faster to maintain resilience. This capability must work round the clock, given that threat actors increasingly look to strike at weekends and during holidays to maximize their efforts. By minimizing dwell time, organizations can reduce the costs associated with an incident. IBM calculates that data breaches last year which took under 200 days to identify and contain incurred costs of $4.32 million, while those with a lifecycle exceeding 200 days had an average cost of $5.65 million.
-
Encourage clearer understanding and better decision making by not bombarding the customer with too much technical information. They need to know what happened, how serious the incident is, what the service provider has done to remediate, and what else needs to be done by their organization. Too much information can cripple response efforts.
-
Deliver stronger operational continuity with a system that supports resilience by preventing incidents where possible, limiting the impact when they do occur, and ensuring the company can maintain minimum viable operations while recovering swiftly. SMBs have a smaller margin of error than large enterprises, making rapid recovery key to preserving customer trust and minimizing the financial impact.
-
Drive faster time to value through rapid onboarding and deployment, ensuring the SMB can start benefiting from the service as soon as possible. AI and automation can help here, and ensure the exposure window is kept as short as possible.
-
Encourage safer AI adoption by ensuring that all AI in use in the organization is managed and governed securely. That means first understanding what is in use in the organization, what data is being fed into it, and — in the case of agents — what it can access. Then working out policies and controls to minimize risk. A secondary layer of protection works to reduce leakage risks and prompt injection or data poisoning so that existing systems can’t be hijacked by malicious third parties.
-
Increase protection across the corporate attack surface, which could include identity, collaboration tools, remote access, AI usage, SaaS apps, cloud infrastructure and more. A trusted provider will help to manage risk across this distributed and complex IT environment, which could stretch from remote employee laptops to cloud servers. Threat actors are past masters at finding gaps in protection, so coverage must be comprehensive.
The common thread running through all of these requirements is the need for security that works quietly in the background, surfaces only what matters, and scales with the organization — without demanding expertise or headcount that most SMBs simply don’t have.