In September, reports emerged that a Virginia woman had been submerged by a flood of emails. Hundreds of automated messages poured in over a 24-hour period, including newsletters and promotions she’d never signed up to. But this was no ordinary spam campaign. The real reason behind the inbox blitz was to bury a legitimate email from the victim’s bank warning her about a fraudulent laptop purchase.
This is email bombing. And if it’s happened to you, it could be a warning sign that your identity or online accounts have been hijacked by fraudsters.
What is email bombing?
Sometimes called “form bombing,” “list bombing,” or “subscription bombing,” email bombing attacks usually follow the same pattern. First, an attacker gets hold of your email address. They could do this from historic data breaches, marketing databases, online leaks, or even a prior phishing attack. Once they have it, they’ll use automated, bot-powered tools to sign you up for hundreds or thousands of legitimate online services like newsletters, subscriptions, mailing lists, free trials, and competitions.
These will each generate a welcome email or similar. And because they are usually legitimate services, they’re often not blocked by spam filters. The result is an inbox overflowing with messages.
Two reasons are behind most email bombing attempts:
- The scammer is trying to distract the victim so that they don’t see a genuine email among all of the artificially generated ones. They may have hijacked one of your accounts and reset the password, triggering a notification to your inbox. Or they may have made a fraudulent purchase in your name, with the invoice subsequently emailed to you. The main point is to create a smokescreen which prevents you from tackling the more serious fraud.
- The hacker may subsequently contact you pretending to be a tech support engineer. They’ll claim to be able to solve your email “problem” and either request a fee to do so, or trick you into installing remote access software so they can take a look at your machine. That could enable them to steal sensitive information on your computer like passwords stored in the browser, or even install additional malware.
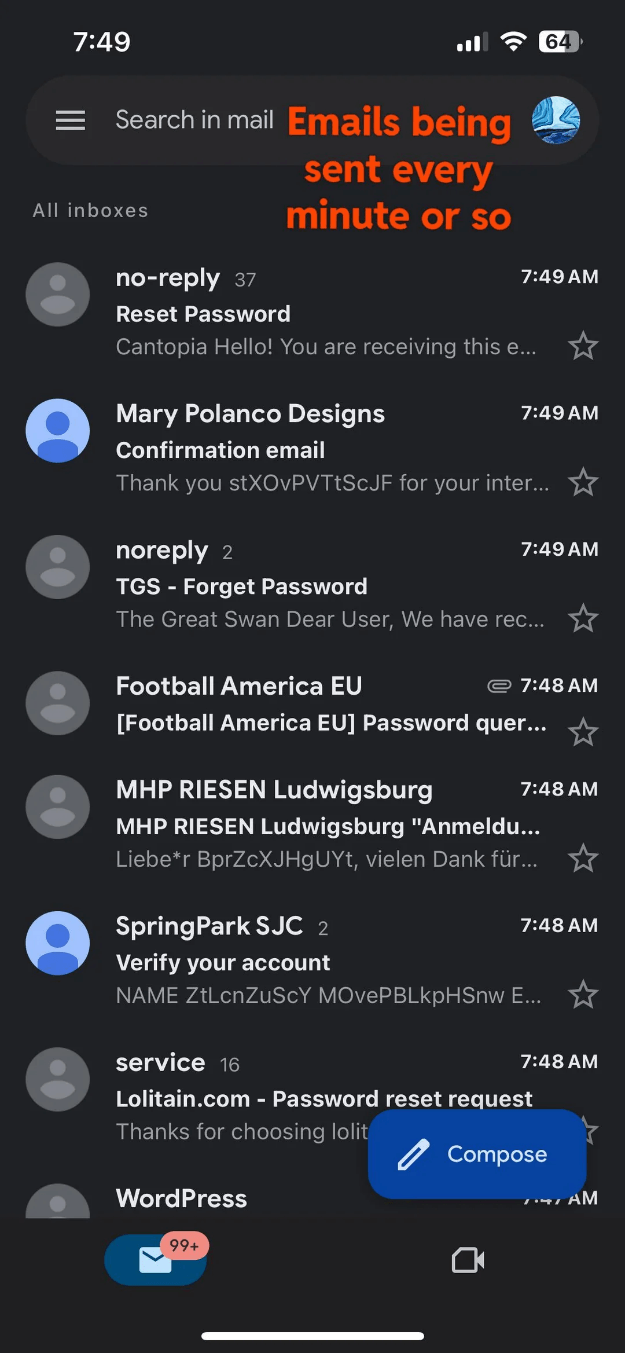 Source: Reddit
In a corporate scenario, the bomber is most likely trying to distract the cybersecurity team from a more serious attack, such as a data breach, a business email compromise, or invoice fraud attempt. Alternatively, they may be trying to disrupt operations as leverage for extortion — ransomware affiliates have used email bombing as a precursor to a fake IT help desk contact in order to gain remote access. It could also be the work of a disgruntled current or former employee.
I’ve been email bombed: what next?
If you’ve logged on to find your inbox overwhelmed, don’t panic. Rather than trying to unsubscribe from all of the random services you’ve been signed up to, focus your energy on finding the threat that your attacker wanted to hide. Search for security alerts, new device sign-ins, email/phone number changes, password changes/resets, or purchases. Look through your spam folder as well as your inbox, in case the message has ended up there.
If you don’t immediately see anything out of the ordinary, check your most sensitive accounts individually. These could include:
- Bank/PayPal/credit card/crypto
- Apple/Google/Microsoft
- Social media accounts
Look for any suspicious activity: new devices or payment methods added, passwords that may have been changed, and/or recovery details altered. It’s also worth checking your email forwarding rules and sent/deleted items folders for anything unusual.
If you notice something suspicious, try to lock the hacker out by changing the password to a unique, strong credential, and enable two-factor authentication (2FA) for extra login security. Ensure the correct recovery email address and phone number are listed, or the attacker may be able to reset the account again. Contact the company itself if you’re concerned about fraud.
Remember to preserve anything related to a possible account takeover or fraud attempt. Only purge when you’re confident the issue is resolved. You can do this more quickly by identifying patterns in the messages — such as common senders, date ranges, or domains — then bulk selecting and deleting in batches.
It goes without saying that you should put the phone down immediately if anyone calls you claiming to be a tech expert who can sort out your email problem.
How to prevent email bombing
Prevention is usually better than cure. While it’s not always possible to stop your email address ending up in the wrong hands, you can limit exposure by ensuring it isn’t listed on public-facing web pages like social media profiles. Also follow security best practices to stay safe from phishing attacks.
Keep your most sensitive accounts as secure as possible. This includes your primary email address, which will be used to receive password reset messages from other online accounts. Use a password manager to ensure they all have strong, unique credentials, and enable 2FA for an extra layer of security via an authenticator app or passkey.
It may also be worth using a secondary email address for less important correspondence like shopping, travel, and other leisure activities. That way, if this account is hit by an email bomb, your most important messages — from banks, government services, healthcare providers, and similar — remain unaffected.
There is no silver bullet to prevent email bombing, but following account security best practices will significantly reduce the risk of your inbox being weaponized against you.
Frequently asked questions
Why is my inbox full of hundreds of sign-up emails?
You may be the victim of an email bomb, also known as a form bomb, list bomb, or subscription bomb. A fraudster has used automated tools to sign your email address up to new services for one of two reasons: either they’re hoping to bury a legitimate security or anti-fraud message, or they’re planning to call you while pretending to be a tech support engineer who can help.
Has my email account been hacked if it’s full of sign-up emails?
Probably not. Fraudsters may have scraped your address from the public web, harvested it from a historic data breach, or bought it from a marketing database. However, the security or fraud event they’re trying to conceal with the email bomb may have involved an account takeover.
My inbox is full of new messages — what should I do?
First, search for the notification the attacker is trying to hide, checking both your inbox and spam folder, and preserve it. Look for security alerts, new device sign-ins, email or phone number changes, password resets, or purchases. If you don’t find anything, check your sensitive accounts — bank, social media, tech platforms — for unusual activity. Change passwords to strong, unique credentials and enable two-factor authentication (2FA) for extra login security.
I’ve been email bombed. Should I unsubscribe from all the new emails?
No. It’s important to first find and preserve the security notification or fraud warning the attacker is trying to hide. Only purge once you’re confident the issue has been resolved. Speed up the process by deleting in batches — search for common senders, date ranges, or domains to bulk-select messages.
What if someone contacts me offering to fix the problem?
They are a fraudster. Their goal is either to charge you a fee or to trick you into installing remote access software on your machine, which could lead to malware infection or data theft. Hang up immediately.